RPA/APA for Cross-System Data Synchronization: Contracts, Failures and Recovery
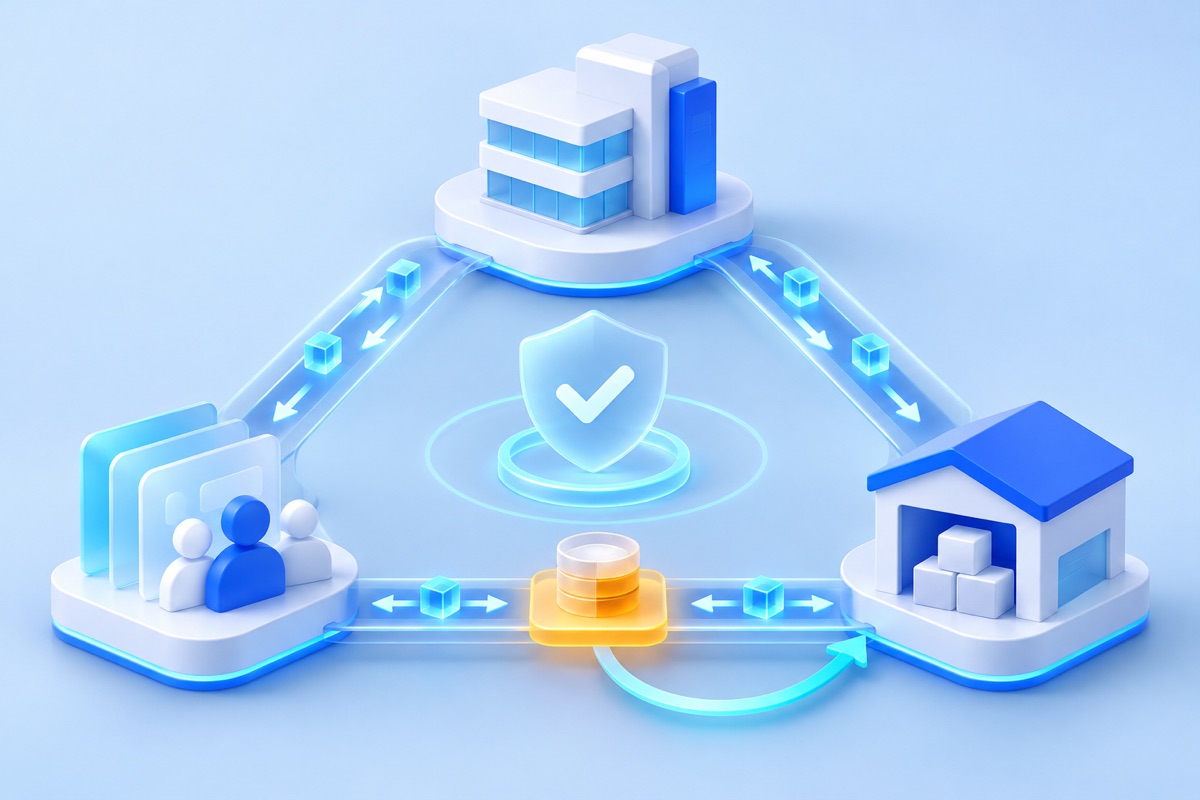
Cross-system synchronisation needs an explicit contract for record identity, field ownership, versions and completion. RPA can operate the required interfaces; APA adds a way to develop, maintain and reuse the process as a callable asset. Neither makes separate systems one atomic transaction. If an ERP update succeeds and a CRM update times out, the caller needs evidence of each outcome and a defined recovery path. The design should establish who may change each field, how repeated requests are recognised and which state another application or agent may safely treat as complete.
- Business contract: object identity, field ownership, approved transformations and conflict handling.
- APA focus: reusable invocation, controlled migration and maintenance of the synchronisation operation.
- Failure model: partial writes, lost updates, schema drift and unknown outcomes.
- Recovery: reconciliation, safe retries, compensating actions or human resolution as appropriate.
Define the object before choosing the sync interval
A customer may have a CRM account identifier, an ERP customer number and a billing account. Similar names do not establish identity, and different identifiers do not prove different organisations.
- Canonical identity: define the business object and how local identifiers map to it.
- Entity boundary: distinguish legal entities, branches, billing accounts and delivery locations where the business needs them separated.
- Field owner: assign the system or process authorised to set each field.
- Transformation rule: define code mapping, date handling, units and the treatment of missing values.
- Conflict owner: name the person or service responsible when rules cannot establish the intended value.
Object mapping: canonical identifier plus the relevant source and target identifiers.
Change identity: a stable request identity and source version or event reference appropriate to the operation.
Completion contract: the target systems and fields that must be verified, including explicit partial or unknown states.
The appropriate request key depends on the business operation. Combining object, field and source version may help in one design, but it does not by itself make a target create operation idempotent.
Field ownership needs a versioned business policy
Synchronisation should apply the organisation's agreed authority model instead of allowing whichever update arrives last to decide the record's meaning.
- Single-owner fields: one source is authoritative; validate changes against its version and scope.
- Merged information: multiple contributions need a reviewed merge rule and a record of conflicts.
- Derived fields: decide where the value is calculated and whether consumers receive the result or recalculate it.
- Creation-time fields: define the approved correction path rather than assuming the initial value can never change.
- Missing values: distinguish absent, unknown, intentionally blank and deletion requests.
A new ownership policy is a business change. A renamed API field or a moved screen control is an implementation change. Keep their reviews separate so a technical repair does not silently alter which system governs the data.
What APA adds to a callable synchronisation process
Laiye APA supports migration of existing workflows, governed process Skills, agent invocation, OpenAPI integration and traceable results. The calling agent plans the task; APA executes the selected process. The customer-sync example below shows the contract and acceptance checks to define for a reusable operation; it is not an API specification.
- Reuse existing operations: assess working CRM reads and ERP updates before replacing them; preserve useful dependencies and business checks during migration.
- Create a bounded capability: expose an approved customer-update operation with explicit identity, fields and version requirements.
- Validate each invocation: establish the caller's rights, allowed field scope and any required approval before execution.
- Return structured business status: distinguish complete, partial, awaiting review and outcome unknown, with target references.
- Maintain the operation: test changed schemas or screen interactions while preserving the approved ownership policy.
An agent can request the capability without inventing a new mapping for every run. It still needs the correct inputs and authorisation, and it must interpret a partial result as partial.
Walk through one partial update before rollout
Consider a hypothetical address update that must reach the CRM and ERP. The following sequence is a design example; it does not assume either application supports distributed transactions.
- Before writing: validate the canonical customer identity, requested address, source version and approval.
- CRM update: apply the authorised change, retain the target reference and read back the resulting state.
- ERP update: attempt the corresponding operation with the appropriate business and request identifiers.
- Lost ERP response: record the outcome as unknown and query existing target state before retrying.
- ERP not updated: use a safe retry, a compensating business action or human resolution according to the agreed recovery policy.
- Completion: report success only when the required targets meet the contract; otherwise return the completed and outstanding parts.
Staging data in one application is not a generic two-phase commit across independent services. Where a multi-step process uses local transactions, compensating actions and retries, it should be designed and tested for the consistency model it actually provides. AWS saga orchestration guidance.
Failure handling must match the target system's capabilities
A process engine cannot create guarantees that a target interface does not support. Check both normal and repeated requests under the chosen API or UI integration.
- Duplicate creation: persist the request identity and target record reference, and use target-side idempotency or a validated lookup-and-create strategy where available.
- Lost update: use supported version checks, conditional writes or an agreed conflict mechanism before overwriting data.
- Schema drift: reject or quarantine invalid mappings rather than silently writing nulls or retired codes.
- Stale snapshot: check record versions and ordering; timestamps alone may not reliably establish precedence.
- Partial completion: retain step-level status and reconcile affected records before declaring the batch complete.
- Unavailable access: stop or route the task according to policy; recovery must respect revoked permissions.
Use observable postconditions. A successful click or HTTP response may be only one part of proving that the intended customer record now holds the approved value.
Documents are another input path, not a fixed share of all sync work
A contract amendment, supplier certificate or order file may introduce values that later flow into business systems. Keep document identity, interpretation and approval connected to the subsequent update.
Our ADP extraction evaluation includes the following purchase-order and invoice tests:
Purchase-order extraction: 800 documents; accuracy of 91.7%, recall of 93.5% and field-level F1 of 92.6%.
Overseas invoice extraction: 1,000 documents; accuracy of 92.3%, recall of 94.1% and F1 of 93.2%.
- Keep provenance: source file and version, extracted field and available page or location evidence.
- Resolve identity: an extracted customer name still needs to map to the intended business object.
- Validate interpretation: an expiry date, amount or address may require business context before it becomes a system change.
- Route uncertainty: missing fields, conflicting documents and unapproved changes should not become plausible default values.
- Measure the pipeline: document quality, approval, target updates and reconciliation are different stages.
These extraction results measure the document stage. Evaluate synchronisation accuracy, correction effort and automatic completion on the local document mix and downstream validation rules.
Recovery and reuse need the same version discipline
A backfill and a replay may invoke the same process with different scopes. Make those scopes explicit so an otherwise valid operation does not change unintended records.
- Replay scope: identify the failed requests or period and exclude effects already confirmed complete.
- Backfill scope: define historical records, approved values and the policy version to apply.
- Correction scope: preserve later legitimate edits before attempting any reversal or compensating update.
- Publication control: review a changed process before exposing it to other callers.
- Evidence: retain identities, versions, target references, validation results and unresolved cases for each run.
- Reconciliation: compare relevant source and target states at a frequency justified by the business requirement.
A callable process is reusable because its contract and responsibilities remain clear, not because every caller can bypass them. Review operational repairs separately from changes to identity, ownership or conflict policy.
Build one bounded path and expand by acceptance evidence
A first deployment should make failures explainable before it maximises coverage. The following sequence is guidance, not a universal timetable:
- Map identity: agree how representative records correspond across systems, including historical duplicates.
- Assign ownership: approve field authority, transformations and conflict routes.
- Start with a bounded direction: choose fields and records for which authority is clear and the outcomes can be checked.
- Exercise failure cases: duplicate requests, lost responses, concurrent edits, invalid codes and revoked access.
- Validate a process change: confirm that a revised mapping or repaired interaction preserves the intended contract.
- Add reverse or merged paths: proceed when the tested consistency, recovery and ownership arrangements meet acceptance criteria, rather than after a fixed month.
- Monitor workload: record unresolved differences, duplicate effects, review effort, replay results and time to restore agreement.
Where a supported integration already meets these requirements, keep it. Evaluate APA when maintained cross-system operations and reusable invocation address a real gap in the existing workflow.
Frequently asked questions
How is RPA used for cross-system data synchronisation?
- It can retrieve values, apply approved mappings and update another system through available interfaces. Reliable operation also needs identity, field ownership, version checks, outcome verification and recovery. Moving data faster does not resolve an ambiguous business contract.
Does APA make updates across applications atomic?
- Do not assume so. A callable process can still complete one update and fail at another. Confirm target transaction support and define partial states, safe retries, compensating actions and reconciliation for the consistency model actually available.
Why does a retry create duplicate records?
- The original request may already have succeeded, or the repeated create may not be recognised. Persist request and target identifiers, use supported idempotency mechanisms and query unknown outcomes. A particular key format alone cannot guarantee duplicate prevention.
What does a synchronisation Skill need to return?
- A useful design returns the request identity, required target outcomes, business references, validation result and unresolved work. Mark partial, pending or unknown outcomes explicitly so a calling agent or application does not treat every invocation as completion.
Can an agent decide which system owns a disputed field?
- It can help surface information, but the synchronisation policy should specify authority and conflict handling. An unresolved ownership question needs the responsible business decision; it should not be settled by whichever tool response or timestamp arrives last.
Should synchronisation be bidirectional from the start?
- Choose scope according to authority, consistency and acceptance evidence. A bounded one-directional path is often easier to validate first. There is no universal one-month waiting rule; merged or reverse paths need their own tested conflict and recovery arrangements.
What should be monitored after go-live?
- Track source-target differences by field, unresolved-item age, duplicate effects, unknown outcomes, replay results and manual correction effort. Use a defined observation window and record scope so the measures describe actual business agreement rather than raw job counts.
Related reading: Laiye APA; How APA works with Laiye Worker.
Implementation note: The customer-update flow and suggested contract are illustrative, not an API specification. Configure identity, permissions, version checks and recovery for the target systems.